Default Firewall Rules exist at the VPC level and are applied to any VM created in a default VPC.
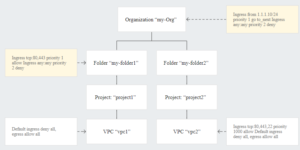
In addition to the firewall rules, GCP has something called Firewall Policies. These are hierarchical.
So - one could use firewall policies to DENY traffic at a higher level - ensuring that any new VM would pick up the DENY.
And then, ALLOW individual VMs that need SSH/RDP access.
Summary
Firewall policies allow more flexibility in applying firewall rules to individual VMs. DENYing at a higher level and ALLOWING at lower levels, would safeguard any new instances being spun up.
