This post will describe how to use network tags to Allow custom port for a specific VM instance on GCP. Also read - Firewall Rules and Policies in GCP.
How do I allow a custom port traffic into a VM?
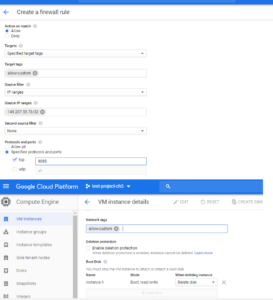
This is the general recipe - 1. Create a firewall rule --> 2. Select the subnet --> 3. Create a target tag --> 4. Attach tag to Compute engine instance
Step 1 - Create a new FW rule with ALLOW on the protocol and TCP port you want to let in.
Step 2 - Select a Subnet
Step 3 - Create an all0w-traffic Network Tag.
Step 4 - Attach the network tag to the VM
Summary
Network tags are a reusable and easy way to work with firewall rules in GCP. This post describes a quick recipe for using network tags to create a firewall rule to let in specific port traffic.
